ShinyHunters steals sensitive FBI data including director Kash Patel’s personal information
Cybercrime gang says it carried out the attack after being "offended" by an FBI warning about its tactics that advised victims not to pay a ransom.
The notorious crime group ShinyHunters has claimed to have stolen a huge cache of highly sensitive personal information belonging to thousands of FBI agents, former employees and job applicants.
Both FBIjobs.gov and the FBI's Special Agent Applicant Portal were reported as unavailable on Tuesday as the agency investigated the incident.
ShinyHunters claims it obtained records covering "almost ALL FBI Agents" as well as people who had applied for jobs at the bureau.
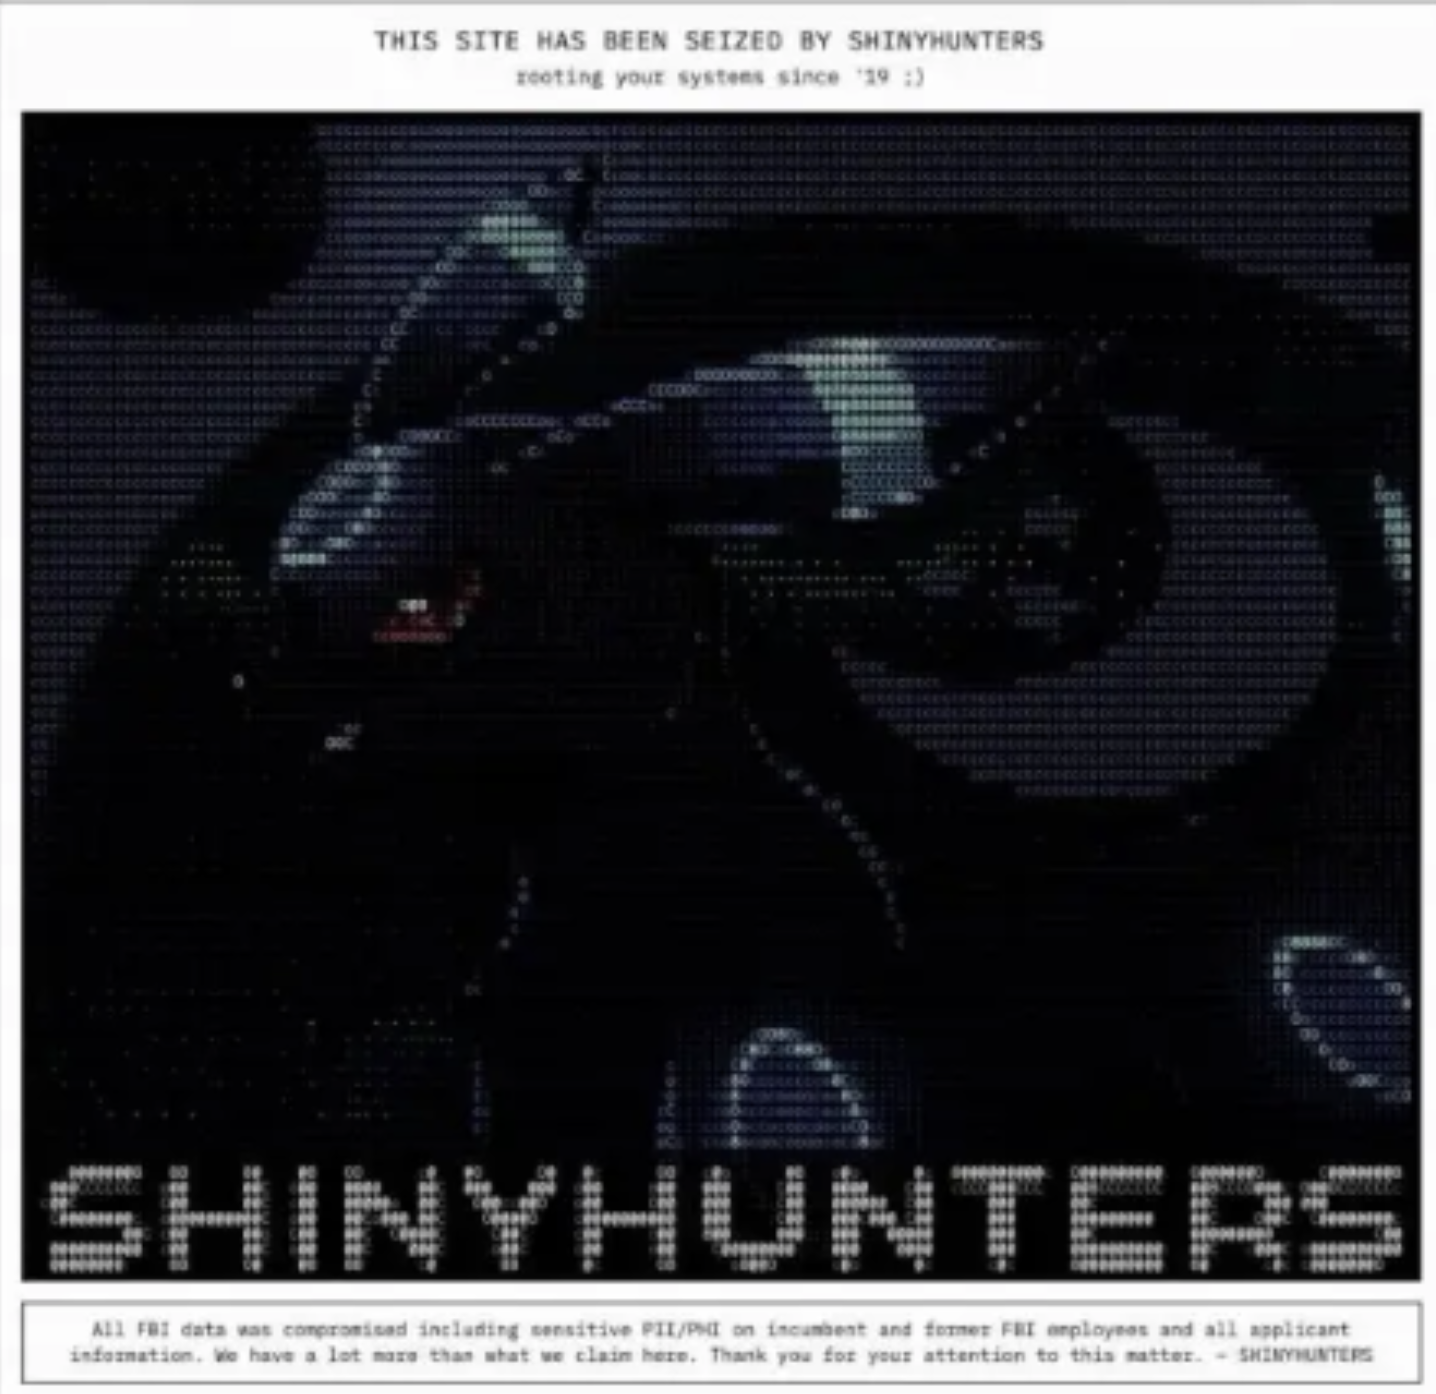
ShinyHunters also defaced the FBI jobs website, which is still down at the time of writing.
The group says the attack was retaliation for an FBI advisory published in May describing its tactics and urging victims not to pay extortion demands.
On its dark web leak site, the gang wrote: "The FBI made substantial false allegations regarding our organization in a FLASH report. We have been severely offended.
"We were very disappointed to see an agency of your standing would resort to such circulation of disinformation in an attempt to 'disrupt' our operations, an effort that ultimately proved unsuccessful.
"For us to properly address and correct these unfounded allegations, we were compelled to adopt a forceful and assertive posture to ensure our response was fully acknowledged."
Stealing a cache of Kash's data
The hackers supplied a sample containing information on roughly 5,000 alleged FBI agents. The records appeared to include names, home addresses, Social Security numbers, work assignments and, in some cases, information about family members.
ShinyHunters has said it gained access through an alleged zero-day flaw in Oracle PeopleSoft running on the FBI's recruitment site, which the group claimed enabled remote code execution on its servers.
"The FBI is aware of claims regarding unauthorized activity affecting FBIjobs.gov and is currently investigating," the bureau said.
The incident was first reported by 404 Media and subsequently investigated by Reuters, which was able to partially authenticate information contained in a sample of the alleged stolen data.
Reuters checked details in the sample against credit bureau records and previously breached information held by dark-web security and intelligence company District 4 Labs.
It found apparent matches in at least 10 cases, including information relating to FBI Director Kash Patel. A source familiar with the matter also told the news agency that some job descriptions matched.
That does not establish where the information was obtained. Reuters could not determine whether the data had actually been taken from internal FBI systems, as ShinyHunters claims.
The dangers of exposing agents' identities
If the stolen information is authentic, the consequences could extend far beyond conventional identity theft. Home addresses, family details and other personal information belonging to federal agents could potentially be exploited for harassment, coercion or targeting.
Rafe Pilling, director of Sophos' Counter Threat Unit, told Machine: "The group has started to share 'proof of life' with data containing personal information of FBI agents and spouses, which could have enduring consequences for those affected.
"Targeting the FBI is exactly the kind of audacious behavior that has come to define this group."
At worst, the data could find its way into the hands of rival nations' intelligence agencies or violent crime gangs.
Andrew Brandt, principal threat intelligence incident commander at Huntress, said: "The FBI handles some of the most serious interstate and transnational crime investigations.
"It doesn't take much imagination to picture scenarios where employees or their families could be threatened or harmed by this kind of information being released.
READ MORE: Cops bring down ancient million-machine Sality botnet after nine-year battle
"The bigger worry is ShinyHunters selling the data to other criminal or nation-state groups who could put it to more damaging use, rather than dumping it themselves. These are law enforcement personnel who deal with serious and dangerous criminals, sometimes requiring infiltration into criminal networks.
"It could be abused in a multitude of ways, from financial fraud to serious threats of harm against staff and their immediate families, to future targeted attacks in cyberspace or the physical world.
"I would imagine the FBI will take this threat pretty seriously, and it could lead to increased efforts to track down and prosecute the actors behind it.
"ShinyHunters must feel pretty confident they won't get caught to threaten a government agency like this.”
Denis Calderone, CTO at Suzu Labs, said the attack aligns with ShinyHunters' "breach, extort, then settle or leak" model, which is unlikely to work with the FBI because it won't pay a ransom.
He continued: "They also say this isn't financially motivated, but I'd take that with a grain of salt. I have a hard time believing terabytes of FBI personnel data just sit on a shelf.
"Foreign intelligence services would love to have it, and having the FBI on their resume makes every future extortion demand more believable, and if the PeopleSoft zero-day is real, the exploit may be worth more than the data.
"Meanwhile, agents and their spouses could have their home addresses posted publicly within a week if this threat is followed through."
Securing against the ShinyHunters zero-day
Defenders have been urged to focus on securing systems so they cannot be compromised by the alleged zero-day used by ShinyHunters.
"If you run PeopleSoft, don't wait for a patch. Get it off the public internet wherever you can, put what has to stay public behind a WAF, and make sure admin components like the /PSEMHUB/ path in their screenshot aren't reachable from outside," Calderone added.
"Hunt for the June indicators and for SSH attempts against the psoft and oracle accounts. Then ask yourself what your applicant portal can reach. At the FBI, a website built for strangers to upload resumes allegedly led straight into GovCloud.”
READ MORE: “LLMs will be subverted”: Malware is evolving to attack AI defenders, SentinelOne warns
Collin Hogue-Spears, senior director of solutions management at Black Duck, also said: "The strategic lesson extends beyond this incident. Internet-facing recruiting portals must operate as narrowly scoped intake systems. They need permission to submit applicant records, not retrieve employee data.
"Organisations must also block public access to PeopleSoft management interfaces. A compromised FBI workload would not automatically constitute an AWS breach, but excessive permissions or exposed administrative functions can turn a public job portal into a path toward the HR system behind it."
"Attention is currency"
So why would ShinyHunters attack a target that's so unlikely to pay out a ransom?
Anna Collard, SVP of Content Strategy and CISO Advisor at KnowBe4, told us the FBI incident looks like "a group performing for an audience, not one driven only by financial motives."
She said: "This alleged breach is a real-world example of something cybercrime researchers have been reporting for a while: for some threat actors, law enforcement attention is status, not risk.
"Dutch researchers found that a formal warning sent to an offender group simply became a badge of honor. And as we put it in our upcoming 'Crime or Career?' report on youth cybercrime across the Global South: 'Where the behavior confers standing, a warning is attention, and attention is their currency.'
"Every 'most dangerous hacker' headline is free advertising: it raises their credibility, raises what victims will pay, and makes them more admirable to the young people at the top of the funnel.
"Much of what drives this is young people chasing status and respect they don't feel they can get any other way. Enforcement still matters, but so does not handing them the stage they're so obviously looking for. The real work is upstream, reaching these kids before a criminal network does."
So is the attack less about ransom and more about reputation?
Dr. Darren Williams, CEO and Founder of BlackFog, said: "Like most ransomware groups, ShinyHunters is highly protective of how it is portrayed. The group has a history of going after individuals who make claims about its activities. It’s no surprise they’ve demanded changes to the FBI’s report because it’s an attempt to control the narrative, however, it’s unlikely to work.”
"If the FBI’s data is extorted, the concern is long-term – who has access to it and what the data could be used for. Cybercriminals have posed as such agencies in order to infiltrate other companies, and depending on the information revealed, the safety of FBI employees.
"This is why the focus has to be on preventing sensitive data being exfiltrated. Encryption can be a distracting smokescreen if the focus is on keeping systems running, but the priority should be preventing sensitive data from leaving the network."